In the financial crime environment, a blacklist is best understood as a control list of persons, entities, accounts, countries, vessels, counterparties, or other identifiers that an institution treats as prohibited, blocked, or subject to heightened restriction. In practice, the term is often used informally. Regulated frameworks usually use more precise terms such as sanctions lists, watchlists, blocked persons lists, or internal prohibited-party lists. For example, OFAC refers to the Specially Designated Nationals and Blocked Persons List (SDN List) and related sanctions lists rather than using the term blacklist.
Key Takeaways
- Blacklists Convert Known Financial Crime Risk Into Operational Restrictions
- Not All Blacklists Have the Same Legal Effect
- Sanctions Lists Differ From Internal Prohibited-Party Lists
- Internal Blacklists Can Help Prevent Repeat Fraud and Re-Onboarding
- Screening Must Extend Beyond Exact Name Matching
- Beneficial Ownership and Control Can Trigger Restrictions
- Aliases and Related Parties Can Complicate Identification
- Blacklist Controls Support AML, Sanctions and Fraud Prevention
- Customer and Payment Screening Should Be Integrated
- Existing Customers May Require Rescreening After List Updates
- Poor List Governance Can Create False Assurance
- Screening Outcomes Must Be Linked to Clear Escalation Rules
- Prohibited-Party Controls Require Accurate and Current Data
- Legal Restrictions Must Be Distinguished From Internal Risk Decisions
- Blacklist Controls Are Most Effective When Embedded Across the Customer Lifecycle
- Strong Governance Is Essential to Defensible List Management
From a professional financial crime perspective, the importance of a blacklist lies in its role as a preventive control. It allows an institution to stop or restrict relationships and transactions involving parties that present unacceptable legal, regulatory, or criminal risk. These may include sanctioned persons, blocked entities, known fraudsters, mule accounts, terminated customers, counterparties linked to suspicious activity, or internal subjects of concern. The FCA’s Financial Crime Guide stresses that firms must maintain effective systems and controls to counter the risk that they might be used to further financial crime, and blacklist-style controls often form part of those systems.
A key distinction is that not all blacklists are the same. Some are external and mandatory, such as sanctions lists maintained by authorities. Others are internal and risk-based, such as a bank’s list of accounts or customers it has exited for fraud, mule activity, or other serious misconduct. The legal effect also differs. Under U.S. sanctions, persons on the SDN List are blocked, and U.S. persons are generally prohibited from engaging in transactions involving them. By contrast, an internal blacklist may reflect a firm’s own decision that a relationship or counterparty should not be accepted or re-onboarded, even where no public designation exists.
Listen the podcast
Watch the video
In the financial crime environment, blacklist controls are especially important because they convert intelligence into an operational decision. A firm may know that a party is sanctioned, linked to prior fraud, or associated with suspicious activity, but unless that knowledge is embedded into screening, onboarding, payments, and case-management processes, the institution may still transact with them. This is why blacklist controls are closely linked to screening systems and stop/go decisioning. OFAC’s Sanctions List Service and Sanctions List Search tool are designed to help users access current sanctions data and search for potential matches, illustrating how these lists are meant to be operationalized rather than merely stored as reference material.
One of the most important professional issues is that blacklist management is not only about exact name matching. Ownership and control matter as well. OFAC’s 50 Percent Rule provides that entities owned 50 percent or more, directly or indirectly, in the aggregate by one or more blocked persons are themselves considered blocked, even if they are not separately named on the SDN List. That means a blacklist-style control framework must often look beyond the listed name and consider beneficial ownership, control structures, aliases, and related parties.
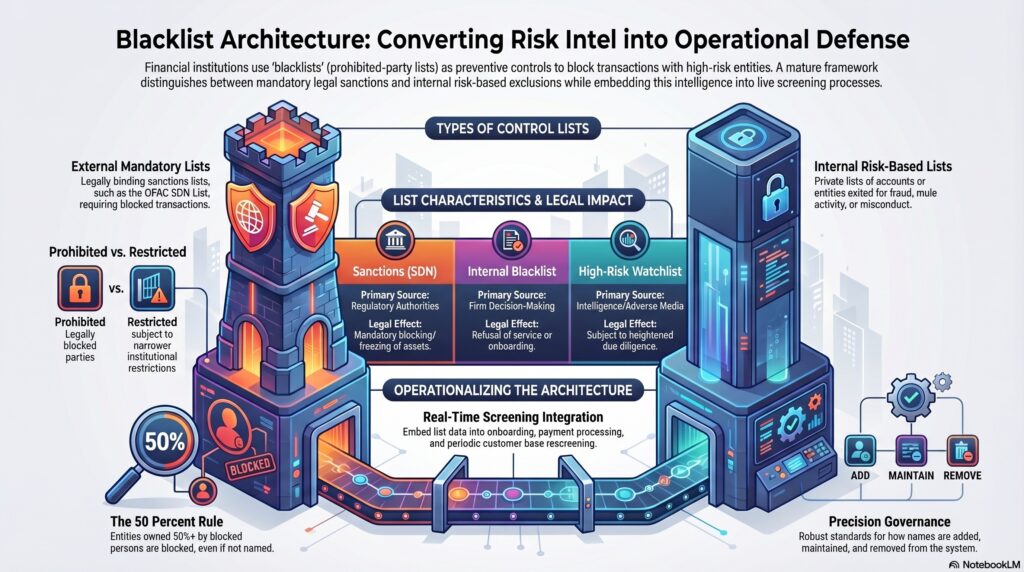
This is why firms should treat blacklist controls as part of a broader screening and due diligence framework rather than as a static file of prohibited names. A mature approach includes sanctions screening, internal adverse-party lists, ownership analysis, escalation standards, and governance over how names are added, maintained, reviewed, and removed. It also requires clear differentiation between a legally blocked party, a non-SDN party subject to narrower restrictions, and an internally prohibited party that the institution has chosen not to serve. OFAC itself maintains multiple sanctions-related lists with different associated prohibitions, which reinforces the need for precision rather than treating every “listed” party identically.
Operationally, blacklist controls are relevant across onboarding, payments, customer due diligence, sanctions compliance, fraud prevention, and case investigations. A customer may be screened against a blacklist at account opening, a payment beneficiary may be checked before funds are released, and an existing customer base may be rescreened when lists are updated. If the control environment is weak, firms may miss blocked parties, process prohibited transactions, or fail to identify repeat fraudsters and related entities. FCA enforcement actions against firms for weak financial crime systems and controls illustrate how failures in monitoring and control design can have major regulatory consequences.
What Financial Institutions Should Consider
- Maintain Clear Governance Over Internal and External Lists
- Distinguish Mandatory Sanctions From Internal Prohibitions
- Screen Customers, Beneficiaries and Counterparties
- Strengthen Alias and Fuzzy-Matching Capabilities
- Assess Beneficial Ownership and Control
- Apply Ownership Rules to Connected Entities
- Re-Screen Existing Customers After Material List Updates
- Integrate Blacklist Screening Into Onboarding
- Integrate Blacklist Screening Into Payment Controls
- Link Confirmed Fraud Intelligence to Internal Prohibited-Party Lists
- Establish Clear Criteria for Adding and Removing Entries
- Maintain Evidence Supporting Internal Blacklist Decisions
- Review Internal Lists Periodically
- Prevent Unauthorised Overrides
- Escalate Potential Matches Promptly
- Maintain Complete Screening Audit Trails
- Monitor False-Positive and False-Negative Risk
- Test Screening Effectiveness Regularly
- Integrate Blacklist Controls With AML, Fraud and Sanctions Governance
- Treat List Management as an Ongoing Financial Crime Control
Ultimately, blacklist is a useful shorthand in the financial crime environment, but the more accurate professional concept is a set of prohibited-party and high-risk-party controls embedded within sanctions, fraud, and AML frameworks. Its value lies in helping firms turn known risk into enforceable operational restrictions. When properly governed, blacklist controls help prevent prohibited relationships, stop suspicious payments, and strengthen the institution’s wider financial crime defenses. When poorly designed, they create false assurance and leave firms exposed to sanctions breaches, fraud recidivism, and wider control failure.