Authorised Push Payment, commonly abbreviated as APP, refers to a bank or account-to-account transfer that is authorised by the payer and pushed from their account to another account. In ordinary use, an APP is simply a legitimate payment instruction. In the financial crime environment, however, the term is most often discussed in the context of APP fraud or APP scams, where the customer is deceived into authorising the transfer to an account controlled by a criminal or to a destination that is not what it appears to be. The FCA describes APP fraud as customers being tricked into sending money to a fraudster via a bank transfer that the customer authorises, and the PSR similarly describes APP scams as cases where someone is tricked into sending money to a fraudster posing as a genuine payee.
Key Takeaways
- Authorized Push Payments Are Legitimate Payment Instructions That Can Be Exploited for Fraud
- Customer Authorization Does Not Necessarily Mean the Payment Is Legitimate
- APP Fraud Relies on Deception Rather Than Direct Account Compromise
- Social Engineering Is Central to Most APP Scams
- Impersonation, Investment, Romance and Purchase Scams Commonly Use APP Payments
- Authentication Alone Cannot Establish Genuine Customer Intent
- Payment Context Is Critical to Identifying APP Risk
- Faster Payments Increase the Speed at Which Fraud Proceeds Can Move
- APP Fraud Frequently Connects to Money Mule Networks
- Receiving Accounts Are a Critical Part of the Fraud Infrastructure
- APP Risk Sits at the Intersection of Fraud, Payments and AML
- Effective Controls Must Operate Before, During and After the Payment
- Behavioural Analytics Can Help Identify Abnormal Payment Journeys
- Payee Verification and Customer Warnings Can Reduce Scam Risk
- Reimbursement Obligations Have Increased the Governance Importance of APP Controls
- APP Fraud Should Be Managed as a Full Payment-Lifecycle Risk
From a professional financial crime perspective, APP is significant because it exposes a critical weakness in traditional payment-control logic: the fact that a payment is customer-authorised does not necessarily mean it is legitimate in substance. In unauthorized fraud, the criminal takes money without the customer’s approval. In APP fraud, the customer becomes the operational mechanism through which the fraud is executed. That makes the typology especially difficult to manage because the payment may pass normal authentication, device, and access controls even though it has been induced by deception. The FCA’s recent guidance consultation explicitly frames APP fraud as a situation in which the payer is deceived into authorising a payment either to an account they wrongly believe belongs to a legitimate payee or for something they wrongly believe is legitimate.
In the financial crime environment, APP should therefore be understood as more than a payment method. It is a control surface through which criminals exploit trust, urgency, fear, and social engineering. The payment itself is only the final stage of the fraud. Before the transfer takes place, the victim may have been manipulated through impersonation, invoice interception, romance grooming, fake investment opportunities, false purchase offers, or claims that their funds are at risk and must be moved to a “safe account.” UK Finance identifies common APP fraud categories including purchase, investment, romance, and impersonation scams, which shows that the typology is broad and adaptable rather than confined to one form of deception.
What makes APP particularly important in modern financial services is the speed and finality of account-to-account payments. In many cases, once an APP transfer has been sent, the funds can move rapidly through receiving accounts, mule networks, or onward payments before the sending institution has a realistic opportunity to recover them. The PSR notes that APP scams are a major issue within Faster Payments in the UK, and its reimbursement framework has been designed specifically because the harm can be severe and recovery difficult once funds have been transferred. In practical terms, this means APP risk sits at the intersection of fraud prevention, payment operations, consumer protection, and anti-money laundering.
Listen the podcast
Watch the video
A professionally mature understanding of APP requires distinguishing between the payment instruction and the criminal manipulation behind it. The customer may log in normally, authenticate successfully, add the payee themselves, and confirm the transfer. From a narrow operational viewpoint, everything may appear valid. The real risk lies in the context of the payment: why it is being made, whether the payee is truly who the customer believes them to be, whether the transaction aligns with normal behaviour, and whether there are indicators of coercion or deception. This is why APP cannot be managed effectively through authentication alone. It requires contextual risk assessment, typology awareness, and strong intervention models at the point where the payment is about to be made.
APP also has a strong connection to money mule activity and wider illicit fund movement. Once a victim authorises the transfer, the receiving account is often under criminal control directly or indirectly, and the funds may then be dispersed quickly to other accounts, converted into cash, moved cross-border, or layered through a wider network. That means an APP case is not only a victim-loss event. It is also part of a broader laundering chain. The PSR has emphasized that both sending and receiving payment service providers have roles in preventing and responding to APP scams, which reflects the fact that the fraud cannot be addressed solely at the point where the victim initiates payment.
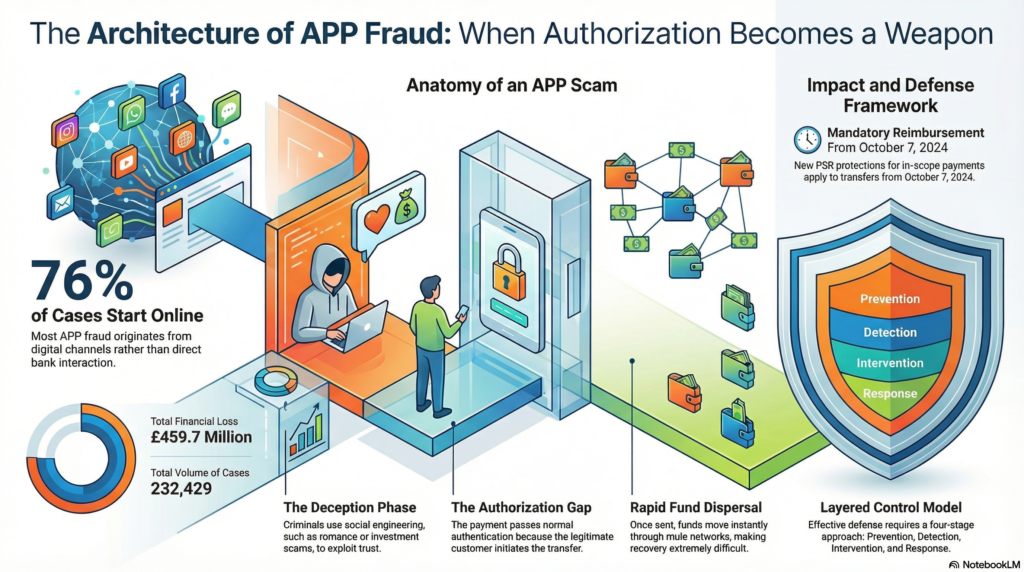
This has major implications for control design. A firm managing APP risk effectively needs layered controls across prevention, detection, intervention, and response. Preventive measures may include clear payment warnings, payee verification tools, stronger friction for unusual transfers, scam education, and customer messaging tailored to current typologies. Detection measures may include behavioural analytics, anomalous payment profiling, device and session context, customer-vulnerability indicators, and intelligence on suspicious receiving accounts. Intervention measures require the institution to act in real time where risk is elevated, including payment delays, challenge prompts, direct customer contact, or further verification before release of funds. Response requires tracing, freezing, reimbursement assessment where applicable, and review of the receiving side for mule or organized fraud indicators. The FCA’s APP guidance consultation is explicitly built around enabling a risk-based approach to these kinds of controls.
Governance is equally important because APP risk now sits within an increasingly formalized regulatory framework in the UK. The PSR states that mandatory reimbursement protections apply to in-scope payments made on or after 7 October 2024, and its subsequent policy materials continue to set out how the reimbursement requirement operates. UK Finance also explains that these protections apply under PSR rules, while noting that reimbursement is not automatic in every case because specific exemptions can apply. This matters from a financial crime standpoint because APP is no longer only a fraud-loss issue; it is also a governance, policy, and customer-outcome issue with direct implications for firms’ control design and accountability.
The scale of APP harm reinforces its significance. UK Finance reported £459.7 million lost to APP fraud in 2023, with 232,429 cases, and also noted that 76% of APP fraud cases originated from online sources. Those figures show that APP is not a niche problem but a major feature of the UK fraud landscape, shaped heavily by digital channels and remote interaction. The fact that so much APP fraud originates online also underlines that effective control requires coordination beyond the payment moment itself, including platform intelligence, customer education, and ecosystem-wide disruption of fraud pathways.
What Financial Institutions Should Consider
- Strengthen APP Fraud Risk Assessments
- Apply Behavioural Analytics to Customer Payment Activity
- Monitor First-Time and High-Risk Beneficiaries
- Apply Risk-Based Friction to Unusual Payments
- Strengthen Confirmation-of-Payee Controls
- Detect Customer Coaching and Social Engineering Indicators
- Integrate Device, Session and Transaction Intelligence
- Use Typology-Specific Customer Warnings
- Monitor Payments Following Unusual Authentication Events
- Strengthen Receiving-Account and Mule Detection
- Identify Multiple Victims Paying Common Beneficiaries
- Detect Rapid Onward Movement of Scam Proceeds
- Maintain Rapid Freezing and Recall Capabilities
- Integrate Fraud, AML and Payments Intelligence
- Apply Customer Vulnerability Considerations
- Maintain Clear APP Reimbursement Governance
- Feed Confirmed Scam Intelligence Back Into Detection Models
- Measure Prevention and Recovery Outcomes
- Assess Customer Intent Rather Than Authentication Alone
- Treat APP Fraud as an Enterprise Financial Crime Risk
Ultimately, Authorised Push Payment is important in the financial crime environment because it represents the point at which deception is converted into the movement of money. The transfer may be customer-authorised, but the criminality lies in how that consent is engineered and in how the receiving side is used to capture and move the proceeds. In a modern financial system built around fast account-to-account payments, APP risk cannot be treated as a narrow customer mistake or a simple payment dispute. It must be understood as a core financial crime issue requiring integrated controls across fraud prevention, payment monitoring, customer protection, mule-account detection, investigations, and governance.


