A professional fraudster is an individual or entity that engages in fraud as a primary or sustained occupation rather than as an isolated opportunistic act. This is not a formal regulatory category in the way that terms like politically exposed person or money services business are. It is mainly an industry typology label. NICE Actimize defines a professional fraudster as an individual who chose or was driven into a criminal career by circumstances, personality, environment, and social situation, while FinCrime Intelligence defines the term more simply as an individual or entity that engages in fraud as a primary occupation.
Key Takeaways
- Professional Fraudsters Treat Fraud as a Repeatable Business Model
- Professional Fraudsters Differ From Opportunistic or One-Time Offenders
- Technical Skill and Strategic Planning Increase Their Effectiveness
- Professional Fraudsters Continuously Adapt to New Controls
- Cybersecurity Expertise Can Support Credential Theft and Account Compromise
- Social Engineering Is a Core Professional Fraud Capability
- Phishing Kits and Malware Can Industrialise Fraud Operations
- Synthetic Identities Can Help Criminals Bypass Onboarding Controls
- Forged Documents Can Be Used to Defeat KYC Verification
- Account Takeover Is a Common Professional Fraud Typology
- Business Email Compromise Can Be Operated at Scale
- Money Mules Help Professional Fraudsters Receive and Move Proceeds
- Fraud Rings Can Divide Criminal Activity Into Specialist Functions
- Criminal Networks Can Operate Across Multiple Industries and Jurisdictions
- Shared Devices, Infrastructure and Identities Can Reveal Fraud Networks
- Fraud Proceeds Can Feed Wider Money Laundering Activity
- Professional Fraudsters Often Learn From Failed Attempts and Control Friction
- Static Fraud Rules Can Be Ineffective Against Adaptive Criminal Behaviour
- Detection Requires Behavioural, Device and Network Intelligence
- Professional Fraud Should Be Treated as an Organised and Continuously Evolving Threat
In the financial crime environment, the term matters because it distinguishes repeat, organized, and practiced fraud actors from more opportunistic offenders such as first-party abusers or occasional “citizen fraudsters.” A professional fraudster is typically more adaptive, more persistent, and more capable of using multiple techniques across channels. They may not rely on one scam or one product weakness; instead, they often move between application fraud, account takeover, phishing-enabled fraud, payment fraud, mule recruitment, synthetic identity abuse, or merchant and refund schemes depending on what the control environment will allow. This is an inference based on the cited glossary definitions and broader industry treatment of fraudsters as persistent criminals rather than one-off offenders.
From a professional perspective, the defining characteristic is not just that the person commits fraud repeatedly, but that fraud appears to function as a deliberate operating model. That usually means the person invests time in learning weaknesses, testing controls, using aliases or networks, exploiting digital channels, and refining methods based on what works. In practice, this can involve stolen credentials, compromised identities, social engineering, false documentation, collusion with mule networks, or orchestration of multiple accounts and counterparties. NICE Actimize’s broader fraud materials and industry commentary on mule networks and modern fraud typologies support the view that serious fraud actors work through coordinated infrastructure rather than isolated deception alone.
Watch on YouTube: Professional Fraudster
This distinction is important because professional fraudsters create a different control problem from opportunistic fraud. Opportunistic abuse may exploit one weak point. A professional fraudster is more likely to probe the institution, adapt to friction, rotate identities or channels, and return after controls change. That means firms cannot rely solely on single-point controls or static fraud rules. They need linked detection, behavioural analytics, cross-channel intelligence, stronger onboarding controls, and investigative processes that connect incidents rather than treating each case as standalone. This is an inference drawn from the nature of repeat criminal activity and the industry framing of modern fraud as adaptive and organized.
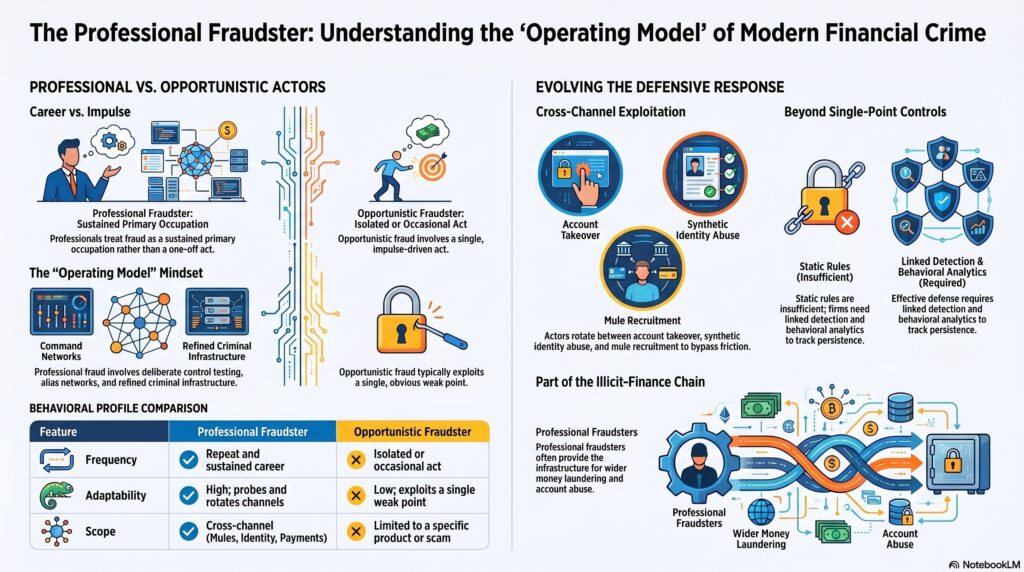
Professional fraudsters are also relevant because they often overlap with the wider financial crime ecosystem. They may recruit or exploit money mules, use false or synthetic identities, rely on phishing or malware to harvest credentials, and move proceeds through accounts or entities that then create AML exposure. In that sense, a professional fraudster is not only a fraud risk; they can also be a source of laundering, account abuse, and wider criminal infrastructure risk. NICE Actimize’s materials on mule networks and suspicious activity reporting support this broader interpretation of fraud as part of a wider illicit-finance chain.
There is also a practical taxonomy issue. Because “professional fraudster” is not a standardized regulatory term, firms should avoid using it as a substitute for more precise underlying typologies in policy or reporting. It is often more useful as a descriptive risk label for a repeat, deliberate, experienced fraud actor than as a technical category on its own. In formal frameworks, firms are usually better served by identifying the actual conduct involved, such as account takeover, first-party fraud, identity fraud, scam enablement, or organized fraud-ring activity. That caution reflects the fact that the term appears mainly in industry glossaries rather than in primary legal or supervisory definitions.
What Financial Institutions Should Consider
- Distinguish Professional Fraud From Isolated Customer Misconduct
- Strengthen Behavioural Analytics Across the Customer Lifecycle
- Integrate Device and Session Intelligence
- Detect Shared Infrastructure Across Multiple Accounts
- Apply Graph Analytics to Identify Fraud Rings
- Monitor Repeated Links Between Identities, Devices and Beneficiaries
- Strengthen Synthetic Identity Detection
- Improve Document and Identity Verification Controls
- Detect Account Takeover and Credential-Stuffing Patterns
- Monitor Business Email Compromise Indicators
- Strengthen Money Mule Detection
- Apply Real-Time Fraud Risk Scoring
- Correlate Onboarding, Login and Transaction Signals
- Integrate Fraud and AML Investigations
- Feed Confirmed Fraud Outcomes Back Into Detection Models
- Use External Fraud and Threat Intelligence Where Permitted
- Monitor Control Evasion and Repeated Failed Attempts
- Conduct Adversarial Testing Against Emerging Fraud Techniques
- Share Intelligence Across Fraud, Cyber, AML and Payments Teams
- Treat Professional Fraud Detection as a Network and Behavioural Intelligence Challenge
Ultimately, a professional fraudster is best understood as a persistent and practiced fraud actor who treats deception as a continuing criminal activity rather than a one-off opportunity. In the financial crime environment, the term is useful because it highlights a class of adversary that is more resilient, more adaptive, and more likely to exploit multiple weaknesses across the customer, payment, and account lifecycle. But because it is an industry term rather than a formal regulatory one, it should be used carefully and backed by clearer underlying typologies when precision matters.


