Identity theft and identity fraud are closely related but not identical concepts. A useful distinction is that identity theftrefers to the unlawful obtaining or misuse of another person’s personal or financial information, while identity fraudrefers to the deceptive use of that identity information to obtain goods, services, funds, or access by false pretences. The FTC defines identity theft as the use of someone’s personal or financial information without permission, and UK reporting guidance distinguishes identity fraud as the use of that stolen identity in criminal activity to obtain goods or services by deception. The U.S. Department of Justice also notes that the terms are often used together to describe crimes involving wrongful acquisition and use of another person’s data.
Key Takeaways
- Identity Theft and Identity Fraud Are Related but Distinct
- Identity Theft Often Precedes Identity Fraud
- Stolen Personal Data Can Enable Multiple Financial Crime Typologies
- Synthetic Identity Fraud Combines Real and Fabricated Information
- Account Takeover Can Result From Stolen Credentials or SIM Swaps
- New Account Fraud Can Exploit Stolen Identities at Onboarding
- Identity Fraud Can Extend to Tax, Healthcare and Benefit Fraud
- Dark Web Markets Facilitate the Sale of Stolen Identity Data
- Inconsistent Customer Information Can Signal Identity Abuse
- New Devices and Geographies Can Indicate Account Compromise
- Early-Life Account Activity Can Reveal Fraudulent Onboarding
- Identity Fraud Creates Both Financial and Reputational Loss
- Strong KYC and CDD Controls Are Central to Prevention
- Ongoing Monitoring Is Required After Onboarding
- Layered Identity Verification Is More Effective Than Single-Signal Controls
- Behavioural and Device Intelligence Strengthen Identity Fraud Detection
- Identity Fraud Risk Must Be Managed Across the Full Customer Lifecycle
- Identity Protection Is a Core Financial Crime Control Domain
In the financial crime environment, the distinction matters because the two concepts often represent different stages of the same criminal process. Identity theft is frequently the precursor event: personal data is stolen, harvested, purchased, intercepted, or otherwise obtained. Identity fraud is then the operational use of that data: opening accounts, applying for credit, resetting credentials, taking over accounts, conducting transactions, or deceiving firms into believing the criminal is the legitimate person. Europol’s public guidance describes identity theft as obtaining enough information about someone’s identity to commit fraud, which aligns closely with this staged interpretation.
From a professional perspective, these typologies are significant because they attack one of the core assumptions on which financial services depend: that the identity presented to the firm is genuine, controlled by the rightful person, and reliable enough to support risk-based decisions. Once that assumption is compromised, multiple downstream controls can weaken at the same time. Customer due diligence may be undermined, onboarding may be corrupted, authentication may be bypassed, transaction monitoring may become less meaningful, and suspicious activity may appear to come from a legitimate customer or account. This is an inference supported by the way official sources describe identity theft as the misuse of personal information for fraud and impersonation.
Watch on YouTube: Identity Fraud and Identity Theft
Identity theft can take many forms. Criminals may steal names, dates of birth, addresses, national identifiers, card numbers, bank details, passwords, or other personal data through phishing, malware, data breaches, document theft, social engineering, mailbox compromise, or account compromise. The theft itself may not create immediate financial loss, but it creates the raw material for later fraud. The FTC and ICO both describe identity theft in terms of personal information being taken and used to impersonate the victim.
Identity fraud is the stage at which that information is put to work. It may involve opening a new account in the victim’s name, applying for loans or services, conducting unauthorized transactions, taking over an existing account, or using the victim’s details to pass verification checks. UK reporting guidance expressly describes identity fraud as using a stolen identity in criminal activity to obtain goods or services by deception. In practical financial crime terms, identity fraud is often the visible manifestation of a wider identity compromise that may have occurred much earlier.
This is why identity fraud and identity theft should be treated as both fraud risks and financial crime enablers. They do not only cause direct losses to victims. They can also support account takeover, application fraud, mule-account creation, payment fraud, and the movement of illicit funds through apparently legitimate customer infrastructure. Europol’s online fraud materials note that theft of personal information can be used for further criminal acts, including identity theft and related abuse.
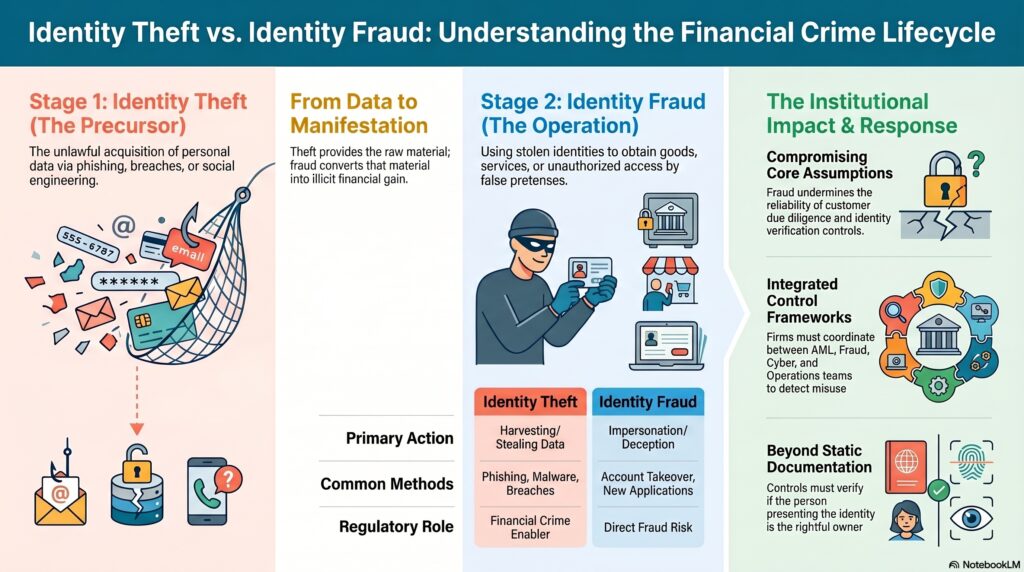
For firms, the control challenge is that identity-based crime often looks credible on the surface. The data may be real, documents may appear valid, and the account activity may initially fit expected patterns. That means strong control frameworks must go beyond static document checks and ask a deeper question: is the person presenting the identity actually the rightful individual, and does the behavior remain consistent with that identity over time? This is an inference from the official definitions and the way identity data is described as being used to impersonate victims and commit fraud.
A mature financial crime response therefore addresses both stages. It seeks to prevent identity theft through data protection, strong authentication, secure account recovery, and customer awareness. It seeks to prevent identity fraud through robust onboarding, identity verification, behavioral monitoring, change-of-details controls, transaction scrutiny, and cross-functional escalation between fraud, AML, cyber, and operations teams. Where identity misuse is suspected, firms also need to consider wider exposure: linked accounts, repeated use of the same identifiers, suspicious payment flows, and possible mule or organized-fraud activity. This is partly an inference from the nature of the typologies described in the cited sources.
What Financial Institutions Should Consider
- Strengthen Identity Verification at Onboarding
- Detect Synthetic Identity Indicators
- Validate Customer Information Across Multiple Sources
- Monitor Changes to Contact and Account Details
- Detect Suspicious New-Device Activity
- Monitor Failed Logins Followed by Successful Access
- Apply Risk-Based Multi-Factor Authentication
- Strengthen Account Takeover Detection
- Integrate Device Fingerprinting and Behavioural Biometrics
- Monitor High-Value Activity Soon After Account Opening
- Detect Mismatches Across Application Data
- Strengthen Document Verification Controls
- Integrate Identity Risk With Transaction Monitoring
- Apply Real-Time Fraud Detection to High-Risk Events
- Monitor Third-Party Identity Verification Providers
- Strengthen Data Protection and Breach Response
- Escalate Identity Fraud for AML Review Where Appropriate
- Feed Confirmed Identity Fraud Back Into Detection Models
- Maintain Clear Customer Re-Authentication Procedures
- Treat Identity Risk as an Ongoing Customer-Lifecycle Control
Ultimately, identity theft and identity fraud are central financial crime risks because they allow criminals to manufacture legitimacy from stolen personal information. Identity theft supplies the data. Identity fraud converts that data into access, money, credit, services, or wider criminal opportunity. In a modern financial system built around remote onboarding, digital servicing, and data-driven decision-making, both typologies demand integrated controls, continuous monitoring, and strong coordination across fraud, AML, compliance, cyber, and customer operations.