Social engineering is the use of deception, manipulation, or impersonation to persuade a person to reveal information, bypass controls, or take an action that benefits the attacker. CISA describes it as tricking someone into revealing information such as a password or taking an action that can expose them to compromise, and its glossary defines it as the use of deception to manipulate individuals into divulging confidential or personal information.
Key Takeaways
- Social Engineering Exploits Human Trust Rather Than Technical Vulnerabilities Alone
- Criminals Use Psychological Manipulation to Influence Victim Behaviour
- Urgency Is a Common Social Engineering Technique
- Authority and Familiarity Can Increase Scam Credibility
- Fear, Reward and Scarcity Can Be Used to Override Normal Judgement
- Social Engineering Is a Core Enabler of Phishing and Vishing
- Bank Impersonation Scams Frequently Depend on Social Engineering
- Authorized Push Payment Fraud Can Result From Victim Manipulation
- Business Email Compromise Often Relies on Trusted Relationships and Routine Processes
- Social Engineering Can Facilitate Credential Theft
- Account Takeover Can Follow Successful Manipulation
- Fraudsters Can Use Personal Data to Create Highly Convincing Approaches
- AI Can Increase the Scale and Personalisation of Social Engineering
- Deepfake Voice and Video Can Strengthen Impersonation Scams
- Authentication Does Not Always Establish Genuine Customer Intent
- Social Engineering Can Target Employees as Well as Customers
- Fraud Proceeds Commonly Move Through Mule Accounts
- Social Engineering Links Cybercrime, Fraud, Identity Crime and Money Laundering
- Customer Education Is Important but Cannot Replace Technical Controls
- Effective Defence Requires Behavioural, identity and transaction intelligence
In the financial crime environment, social engineering matters because it targets the human control layer rather than the technical one. A criminal may not need to defeat encryption, break a system, or steal a device if they can instead persuade an employee, customer, or third party to hand over credentials, approve a payment, reset an account, or trust a false instruction. CISA notes that attackers use human interaction and social skills to obtain or compromise information, and the FTC’s business guidance explains that scammers often create urgency or fear while pretending to be a trusted source such as a senior employee or familiar organization.
From a professional perspective, social engineering is not a narrow cyber term. It is a core fraud and financial crime enabler. Phishing, impersonation scams, business email compromise, tech-support scams, romance scams, fake invoice requests, and account-recovery fraud all depend on some form of social engineering. The FTC’s phishing materials explain that phishing messages aim to get victims to provide personal information or access, while FATF’s recent cyber-enabled fraud paper says digitalisation has accelerated increasingly sophisticated social engineering schemes.
Watch on YouTube: Social Engineering
This is why social engineering is so important operationally. It can compromise several parts of the financial crime framework at once. It may defeat authentication by capturing passwords or one-time codes. It may undermine payments controls by tricking a victim into authorizing a transfer. It may weaken customer due diligence and identity controls by obtaining stolen personal data. It may also compromise internal escalation or supervisory processes if employees are manipulated into overriding normal controls. FATF’s cyber-enabled fraud work explicitly links deceptive social engineering techniques to illicit financial flows and broader AML/CFT concerns.
A key feature of social engineering is impersonation of trust. The attacker typically claims to be someone the victim is expected to trust: a bank, regulator, supplier, colleague, senior manager, telecom provider, or government body. The FTC notes that phishing messages often appear to come from a well-known source, while CISA’s glossary describes phishing as a social engineering technique where threat actors send convincing communications to trick individuals into clicking, sharing, or responding.
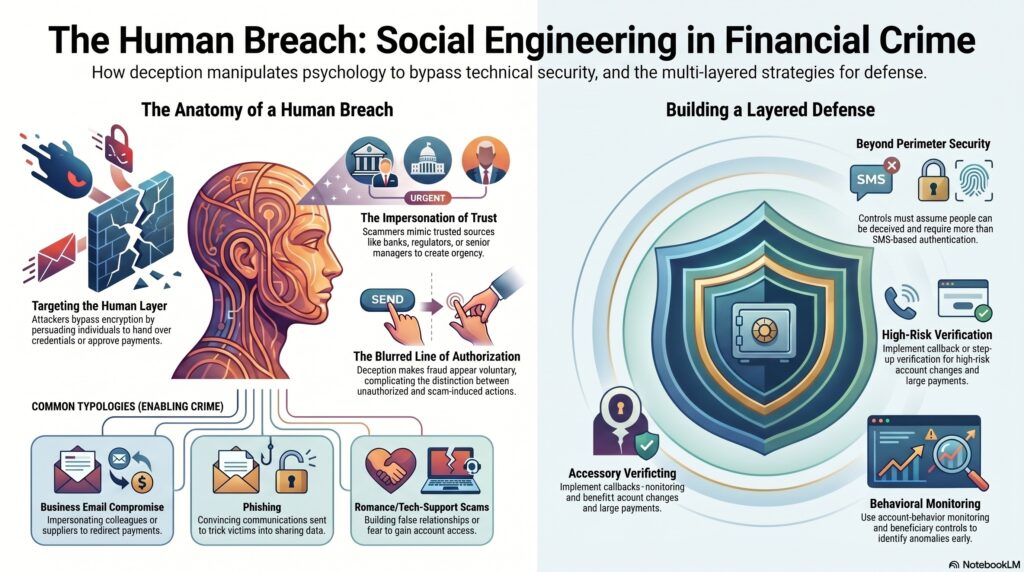
In financial crime terms, social engineering is especially dangerous because it can make a fraudulent action appear voluntary or authorized. A victim may initiate a payment themselves, disclose security details directly, or confirm a fraudulent request because they believe the request is genuine. That blurs the line between unauthorized compromise and scam-induced authorization, which is why social engineering is central to APP fraud, business email compromise, SIM-swap-related account takeover, and many other typologies. This is an inference supported by the FTC’s and CISA’s descriptions of how attackers manipulate victims into acting against their own interests.
A mature control response therefore cannot rely only on perimeter technology. It needs layered controls that assume people can be deceived. These include stronger-than-SMS authentication, callback or step-up verification for high-risk changes or payments, clear customer and employee awareness training, account-behavior monitoring, beneficiary controls, and rapid incident-response processes. CISA’s phishing and social engineering guidance emphasizes recognition and reporting, which reflects the importance of early interruption before the deception turns into account compromise or loss.
What Financial Institutions Should Consider
- Integrate Social Engineering Risk Into Fraud Assessments
- Detect Unusual Payment Behaviour Before Execution
- Apply Behavioural Analytics to High-Risk Payment Journeys
- Strengthen Controls Around New Beneficiaries
- Monitor Sudden Changes in Customer Contact Details
- Detect Account Takeover Indicators
- Reduce Reliance on SMS-Based Authentication
- Apply Step-Up Authentication to Sensitive Actions
- Use Contextual Warnings for Higher-Risk Payments
- Strengthen Call Centre Impersonation Controls
- Monitor Business Email Compromise Indicators
- Train Employees to Recognise Manipulation Techniques
- Establish Independent Verification for Sensitive Requests
- Strengthen Receiving-Account and Mule Detection
- Integrate Device and Session Intelligence
- Correlate Cyber Events With Payment Activity
- Feed Confirmed Scam Outcomes Back Into Detection Models
- Monitor AI-Enabled Impersonation Techniques
- Coordinate Fraud, Cyber, AML and Payments Teams
- Treat Social Engineering as an End-to-End Financial Crime Threat
Ultimately, social engineering is a core concept in the financial crime environment because it converts trust, urgency, and human judgment into a pathway for fraud, account abuse, identity compromise, and illicit fund movement. It is often the first step in a wider financial crime chain. For that reason, social engineering should be understood not just as a cybersecurity problem, but as a foundational fraud and financial crime technique that cuts across customer protection, AML, payments, and internal controls.