Rule-based alerting systems are monitoring tools that generate alerts when predefined rules, scenarios, thresholds, or logic conditions are met. In the financial crime environment, they are commonly used to identify potentially suspicious activity in transaction monitoring, sanctions screening, fraud detection, and communications surveillance. NICE Actimize defines rule-based alerting systems as applications and tools designed to detect misconduct in electronic and audio communications using a set of defined rule functions, and the FCA’s 2024 Financial Crime Guide updates refer specifically to threshold-based, rule-driven transaction monitoring systems.
Key Takeaways
- Rule-Based Alerting Systems Convert Known Risk Indicators Into Operational Alerts
- Predefined Rules, Thresholds and Scenarios Drive Alert Generation
- Transaction Monitoring Is a Core Rule-Based Alerting Use Case
- Sanctions Screening Can Rely on Rule-Based Logic
- Fraud Detection Frequently Uses Rules to Identify Known Attack Patterns
- Communications Surveillance Can Use Rule Functions and Lexicon-Based Logic
- Rule-Based Systems Are Most Effective Against Known and Well-Defined Typologies
- Explainability Is a Major Strength of Rule-Based Detection
- Investigators Can Usually Identify Exactly Why an Alert Was Generated
- Poor Calibration Can Produce Excessive False Positives
- Overly Narrow Rules Can Increase False-Negative Risk
- Thresholds Should Reflect Customer, Product and Transaction Risk
- Segmentation Can Improve Rule Precision
- Static Rules Can Become Less Effective as Criminal Behaviour Evolves
- Rule Libraries Require Regular Tuning and Scenario Review
- Investigation Outcomes Should Feed Back Into Rule Calibration
- Rule-Based Systems Can Be Combined With Behavioural Analytics and Machine Learning
- Alert Volume Alone Is Not a Measure of Control Effectiveness
- Governance, Testing and Change Management Are Critical
- Effective Rule-Based Alerting Requires Continuous Alignment With the Institution’s Risk Profile
From a professional perspective, rule-based alerting is one of the most established control methods in financial crime operations. The core idea is simple: if activity matches a known red flag pattern, exceeds a defined threshold, or breaches a control rule, the system produces an alert for review. That makes rule-based systems especially useful where the firm can clearly describe the risk it wants to detect, such as unusually large cash movement, payments to sanctioned parties, repeated failed authentication, rapid account turnover, or suspicious communications language. The FCA’s recent guidance updates explicitly discuss tailoring and testing transaction monitoring systems and evaluating outcomes such as false positives and intelligence value.
In the financial crime environment, rule-based alerting systems matter because they translate policy and risk appetite into operational detection. A firm may know that certain customer behaviors, transaction patterns, or communications signals are concerning, but unless those concerns are turned into actionable monitoring logic, the risk remains theoretical. Rule-based systems provide that operational bridge. They are particularly common where firms need auditability, explainability, and direct linkage between control design and alert generation. This is an inference supported by the FCA’s focus on rule rationale, calibration, and performance outcomes.
Watch on YouTube: Rule-Based Alerting Systems
A major strength of rule-based alerting systems is clarity. Firms can usually explain why an alert fired, which rule was triggered, what threshold was exceeded, and what typology or risk indicator the rule is meant to capture. That is valuable in regulated environments because controls need to be understandable, reviewable, and defensible. It also makes rule changes easier to document and test than some more complex model-based methods. This is an inference from the FCA’s emphasis on firms being able to articulate the rationale for rules and scenarios.
At the same time, rule-based alerting systems have important limitations. They work best against known or reasonably well-defined patterns. They are less effective when criminal behavior is adaptive, subtle, spread across multiple channels, or unlike anything the firm has encoded into its rules. Poorly calibrated systems can generate excessive false positives or miss meaningful suspicious activity altogether. The FCA’s poor-practice example expressly highlights a threshold-based, rule-driven transaction monitoring system that was poorly calibrated, with the firm unable to explain the rationale for particular rules and scenarios.
This means calibration is critical. A rule that is too broad may overwhelm investigators with low-value alerts. A rule that is too narrow may create false comfort while missing real risk. The FCA’s updated guidance stresses tailoring and testing monitoring systems and considering performance outcomes such as intelligence value and false-positive rates. In practice, good rule-based alerting depends not just on writing rules, but on periodic tuning, segmentation, threshold review, scenario testing, and feedback from investigations.
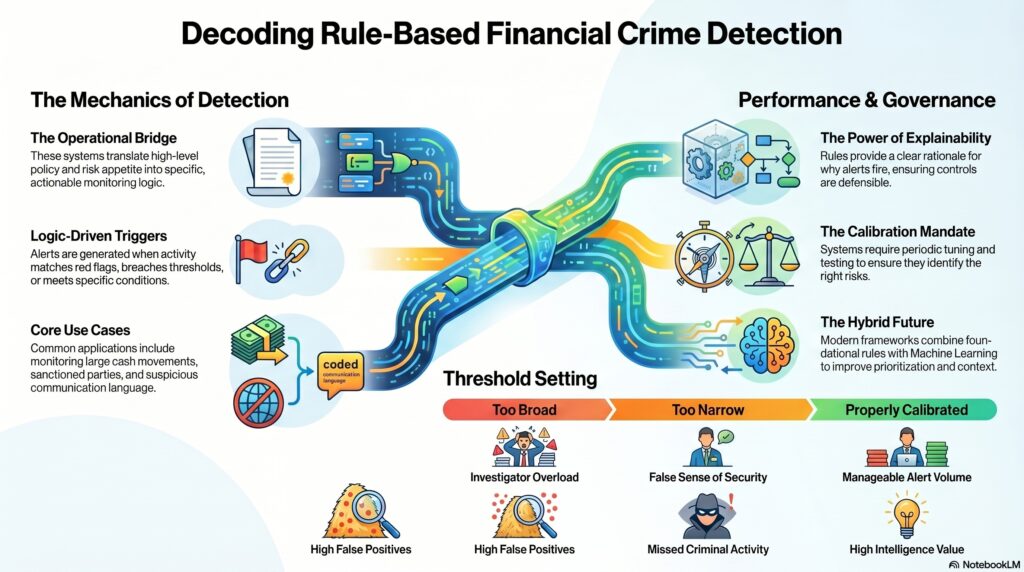
Rule-based alerting systems are also increasingly used alongside other methods rather than on their own. NICE Actimize’s transaction monitoring overview describes modern software as using rules-based logic and often machine learning together, and the FCA’s 2024 policy work refers to supporting responsible innovation and newer approaches such as AI in financial crime monitoring. That reflects the current industry direction: rules remain foundational, but firms often combine them with behavioral analytics, scoring, or machine learning to improve prioritization and context.
Governance is a core issue here. A mature rule-based alerting framework needs clear ownership over scenario design, threshold setting, change management, quality assurance, escalation, and outcome monitoring. Senior management should understand whether the rules are identifying the right risks, whether alert volumes are manageable, and whether the system still fits the business model and risk profile. Without that governance, a rule-based system can become a static library of legacy scenarios that no longer reflects actual risk. This is an inference supported by the FCA’s focus on testing, rationale, and performance outcomes.
What Financial Institutions Should Consider
- Define Clear Ownership of Rules and Scenarios
- Document the Risk Rationale for Each Rule
- Link Rules to Specific Financial Crime Typologies
- Segment Thresholds by Customer and Product Risk
- Calibrate Rules Against Expected Behaviour
- Monitor False-Positive and False-Negative Rates
- Review Alert Volumes and Investigator Capacity
- Conduct Regular Scenario Effectiveness Testing
- Retire Obsolete or Low-Value Rules
- Tune Thresholds Based on Investigation Outcomes
- Maintain Formal Rule Change-Control Procedures
- Preserve Complete Rule and Calibration Audit Trails
- Test Rules Against Emerging Criminal Typologies
- Integrate Rule-Based Alerts With Customer Risk Profiles
- Combine Rules With Behavioural Analytics Where Appropriate
- Use Machine Learning to Complement Rather Than Blindly Replace Rules
- Prioritise Alerts Based on Risk and Intelligence Value
- Monitor Legacy Scenarios for Deteriorating Effectiveness
- Provide Senior Management With Meaningful Detection MI
- Treat Rule-Based Alerting as a Continuously Governed Detection Capability
Ultimately, rule-based alerting systems are important in the financial crime environment because they provide a practical, explainable way to turn known risk indicators into actionable alerts. They remain a core part of transaction monitoring, communications surveillance, and wider detection frameworks. But their effectiveness depends on calibration, testing, governance, and a willingness to refine them as threats and business activity evolve.