A SIM swap scam is a fraud in which a criminal persuades or tricks a mobile carrier into transferring a victim’s phone number to a SIM card or device controlled by the criminal. The FCC describes SIM swapping as scammers covertly swapping SIM cards to a new device without physical control of the victim’s phone, and the FTC explains that the purpose is often to take over accounts that rely on text-message authentication.
Key Takeaways
- SIM Swap Scams Hijack a Victim’s Mobile Number
- Criminals Can Manipulate Mobile Carriers Into Transferring Numbers to Devices They Control
- SIM Swapping Turns a Phone Number Into a Digital Identity Compromise
- SMS One-Time Passcodes Can Be Intercepted After a Successful SIM Swap FinCrime Intelligence
- Password Reset and Account Recovery Processes Can Be Exploited
- SIM Swaps Can Enable Account Takeover
- Bank and Payment Accounts Can Be Drained After Authentication Is Compromised
- Crypto Accounts Can Also Be Targeted Through SIM-Based Account Recovery
- Valid SMS Authentication Does Not Necessarily Prove Genuine Customer Control FinCrime Intelligence
- Social Engineering Is Often More Important Than Technical Hacking
- Stolen Personal Information Can Help Criminals Impersonate Victims to Mobile Carriers
- Phishing and Data Breaches Can Provide Information Used in SIM Swap Attacks
- SIM Swap Fraud Sits at the Intersection of Telecom Fraud, Identity Fraud and Payment Fraud
- Business Email and Other Digital Accounts Can Become Secondary Targets
- Changes to Security Settings Can Help Criminals Maintain Account Control
- Fraud Proceeds Can Rapidly Move Into Mule Accounts
- SMS-Based Authentication Alone Is Insufficient for Higher-Risk Actions FinCrime Intelligence
- Stronger Authentication Methods Can Reduce SIM Swap Exposure
- Rapid Detection Is Critical Because Fraud Can Escalate Immediately After Number Compromise
- SIM Swap Scams Should Be Treated as Gateway Events to Wider Financial Crime
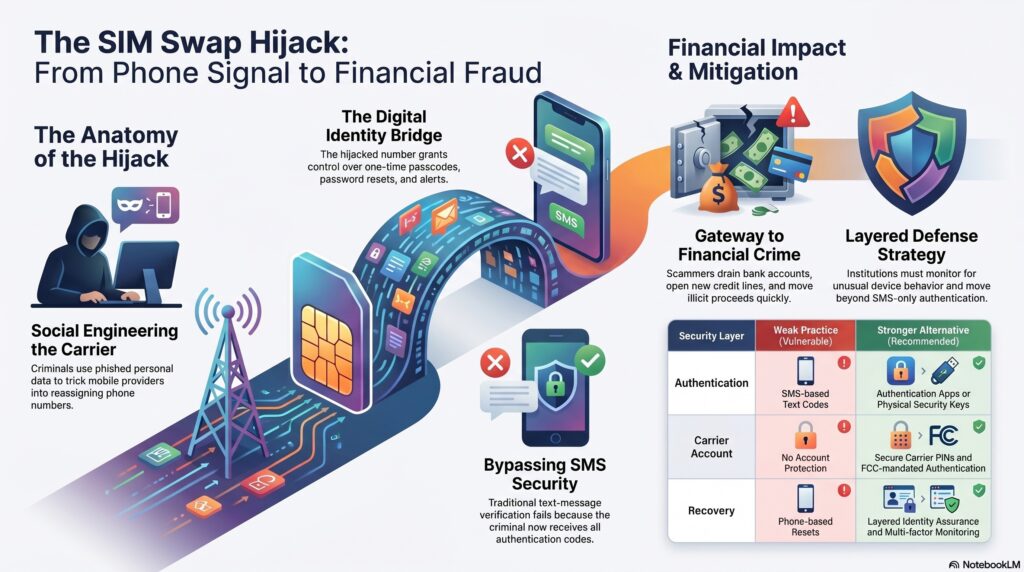
In the financial crime environment, SIM swap scams matter because the mobile number often functions as a digital identity bridge. It is used for one-time passcodes, password resets, account recovery, customer verification, and alerts from banks, payment providers, and crypto platforms. Once a criminal controls the number, they may intercept SMS codes and reset credentials, which can enable account takeover and fraudulent payments. The FTC specifically warns that text-message verification may not stop a SIM swap and advises using stronger alternatives such as an authentication app or security key.
From a professional perspective, a SIM swap scam is not just telecom fraud. It is a financial crime enabler. The compromise at the mobile-carrier level is often only the first step. The next stage may involve draining bank or payment accounts, opening new accounts, taking over email or crypto accounts, or changing security settings so the victim loses control. FATF’s cyber-enabled fraud work notes that cyber-enabled fraud generates large volumes of illicit proceeds and that criminals use compromised access and impersonation techniques to make fraudulent transactions and drain victims’ accounts.
Watch on YouTube: SIM Swap Scam
This is why SIM swap scams sit very close to account takeover, identity fraud, and payment fraud. The fraudster does not always need to break into the bank directly if they can instead compromise the phone-number layer that many institutions still use for authentication or recovery. The FCC’s consumer materials pair SIM swapping with port-out fraud as scams that commandeer the victim’s cell-phone account, while CISA’s mobile security guidance recommends adding a carrier PIN and moving away from weaker authentication practices to reduce SIM-swapping risk.
A key operational issue is that SIM swap scams often rely on social engineering rather than highly technical intrusion. The criminal may impersonate the victim with personal information obtained from breaches, phishing, or other open-source collection, and then convince the carrier to reassign the number. The FCC’s 2023 rules were adopted specifically to strengthen protections against these scams by requiring wireless providers to use secure methods of authenticating customers before SIM changes and number ports.
For financial institutions, the control challenge is that the fraud may initially appear as a legitimate customer interaction. A reset request, login attempt, or payment instruction may be accompanied by the correct SMS code because the criminal now controls the number. That means firms cannot rely too heavily on SMS-based authentication for high-risk actions. The FTC recommends stronger authentication methods, and CISA’s current mobile guidance similarly points users toward stronger account protections.
SIM swap scams are also relevant to the wider AML and proceeds-of-crime framework because the stolen funds often move quickly once access is gained. FATF’s cyber-enabled fraud materials emphasize the links between fraud and illicit financial flows, including the movement of proceeds through accounts and other channels after the initial compromise. In practice, that means a SIM swap event can quickly become a mule-account, suspicious-payment, or fraud-proceeds problem, not just a customer-security incident.
A mature control response therefore needs to be layered. It should include stronger-than-SMS authentication for sensitive actions, monitoring for unusual changes to contact details or device behavior, rapid response procedures when a phone number appears compromised, and customer guidance on carrier account PINs and account recovery. The FCC’s consumer tip card says victims should contact their phone company and their financial institutions immediately, and the FTC likewise advises checking bank and card accounts and reporting unauthorized activity quickly.
What Financial Institutions Should Consider
- Reduce Reliance on SMS-Based Authentication for Higher-Risk Actions
- Deploy Phishing-Resistant Authentication Where Appropriate
- Strengthen Account Recovery Controls
- Monitor Recent Changes to Customer Phone Numbers
- Apply Additional Controls After Contact Detail Changes
- Detect Unusual Device Changes Around Authentication Events
- Integrate Device Intelligence Into Fraud Detection
- Apply Behavioural Analytics to Login and Payment Journeys
- Monitor Password Resets Followed by High-Risk Transactions
- Detect Sudden Changes to Security Settings
- Apply Step-Up Authentication to Sensitive Actions
- Monitor New Beneficiaries After Authentication Changes
- Detect Rapid Payments Following Contact Detail Changes
- Strengthen Account Takeover Detection
- Integrate Telecom and SIM-Swap Risk Signals Where Available
- Establish Rapid Response Procedures for Reported Number Compromise
- Monitor Receiving Accounts for Mule Activity
- Connect Fraud, Cyber, Identity and AML Intelligence
- Feed Confirmed SIM Swap Cases Back Into Detection Models
- Treat Mobile Number Changes as Potential Identity-Risk Events Rather Than Routine Profile Updates
Ultimately, a SIM swap scam is significant in the financial crime environment because it turns control of a phone number into control over digital identity, authentication, and often money movement. It is a gateway fraud: once the number is compromised, wider account takeover and payment fraud can follow quickly. For that reason, it should be treated as a serious cross-functional risk spanning telecom security, identity assurance, fraud prevention, and financial crime response.


