The second line of defense is the part of the organization that provides oversight, challenge, guidance, and monitoring over how the business manages risk. In the IIA’s Three Lines Model, second-line roles assist with managing risk and often focus on areas such as compliance with laws and regulations, controls, information security, and broader risk management. The Bank of England’s current regulatory expectations describe the second line as independent risk management units that monitor the first line.
Key Takeaways
- The Second Line of Defense Provides Independent Risk Oversight and Challenge
- Compliance and Financial Crime Functions Commonly Sit Within the Second Line
- The Second Line Does Not Replace First-Line Risk Ownership
- Business Functions Remain Responsible for Managing Risks They Create
- The Second Line Interprets Regulatory and Financial Crime Requirements
- Policy and Standards Setting Are Core Second-Line Responsibilities
- AML Oversight Is a Key Second-Line Financial Crime Function
- Sanctions Governance Commonly Falls Within Second-Line Responsibilities
- Financial Crime Advisory Supports Higher-Risk Business Decisions
- Second-Line Functions Review Risk Assessments and Control Frameworks
- Independent Challenge Helps Counterbalance Commercial Pressure
- Control Effectiveness Monitoring Is Central to Second-Line Oversight
- Suspicious Activity Governance Can Require Second-Line Oversight
- Management Information Supports Independent Risk Assessment
- Material Control Weaknesses Should Be Escalated to Senior Management
- Strong Second-Line Functions Require Appropriate Authority and Independence
- Excessive Operational Involvement Can Blur First- and Second-Line Accountability
- Excessive Distance From the Business Can Reduce Second-Line Effectiveness
- Coordination Across the Three Lines Strengthens Financial Crime Governance
- Effective Second-Line Oversight Helps Ensure Financial Crime Controls Operate Credibly in Practice
In the financial crime environment, the second line is significant because it sits between the business’s day-to-day risk ownership and the independent assurance provided by internal audit. It does not usually own customer relationships, execute payments, book trades, or onboard clients in the way the first line does. Instead, it helps ensure that those activities are being carried out within the firm’s financial crime framework and in line with legal and regulatory expectations. This is why compliance, financial crime advisory, AML oversight, sanctions governance, and enterprise risk functions are commonly treated as second-line roles.
From a professional perspective, the second line is not there to “do the business’s job for it.” Responsibility for managing risk remains with the first line. The IIA is explicit that responsibility for managing risk remains part of first-line roles, even where second-line specialists provide support, monitoring, and challenge. That distinction matters in financial crime because firms often weaken their framework when the business assumes compliance “owns” AML, fraud, or sanctions risk outright.
Watch on YouTube: Second Line of Defense
In practical terms, the second line of defense in the financial crime environment often performs several core functions. It interprets legal and regulatory requirements, sets policy and standards, advises the business on higher-risk cases, reviews business-wide and customer risk assessments, monitors the effectiveness of controls, challenges first-line decisions, oversees suspicious activity governance, and reports key risks and weaknesses to senior management. The FCA’s Financial Crime Guide is built around the expectation that firms maintain effective systems and controls to counter financial crime, which is the environment in which second-line oversight operates.
This makes the second line especially important where the business faces tension between commercial objectives and control discipline. A front-office team may want to onboard a profitable client, maintain a higher-risk relationship, or process urgent activity quickly. The second line’s role is to test whether the rationale is sound, whether the controls are adequate, and whether the decision fits the firm’s risk appetite and regulatory obligations. In that sense, the second line is a key source of structured challenge in the financial crime framework. This is an inference supported by the IIA model’s emphasis on complementary expertise, support, monitoring, and challenge.
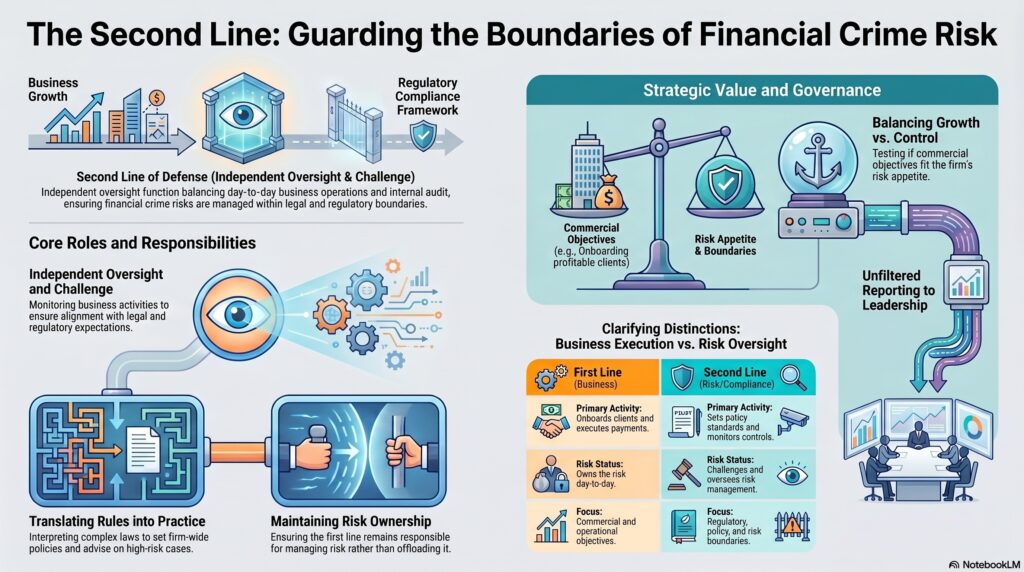
The second line is also central to governance and management information. Senior management and boards need a view of financial crime risk that is not filtered only through business ownership. Second-line functions help provide that view by monitoring trends, identifying weaknesses, escalating breaches or control failures, and assessing whether the first line is operating within policy and appetite. The Bank of England’s 2026 expectations state that monitoring activities are performed independently by the second line where firms adopt the three-lines model.
A mature framework therefore requires the second line to be both independent enough to challenge and connected enough to be useful. If it becomes too operational, it can blur accountability and weaken first-line ownership. If it becomes too remote, it may fail to influence real decisions. The IIA’s Three Lines Model emphasizes coordination and communication across roles rather than treating the lines as isolated silos.
What Financial Institutions Should Consider
- Define Clear First- and Second-Line Responsibilities
- Preserve First-Line Ownership of Financial Crime Risk
- Establish Independent Second-Line Reporting Lines
- Provide Compliance With Sufficient Authority and Resources
- Maintain Direct Escalation Routes to Senior Management
- Establish Clear Financial Crime Policies and Standards
- Challenge Higher-Risk Customer and Transaction Decisions
- Review Enterprise-Wide Financial Crime Risk Assessments
- Monitor Customer Risk Assessment Effectiveness
- Oversee AML and Sanctions Control Frameworks
- Conduct Independent Monitoring of First-Line Controls
- Assess Transaction Monitoring Effectiveness
- Review Sanctions Screening Effectiveness
- Challenge Control Exceptions and Risk Acceptances
- Escalate Material Breaches and Control Failures
- Maintain Effective Financial Crime Management Information
- Track Remediation Actions to Completion
- Avoid Transferring Operational Risk Ownership to Compliance
- Coordinate Effectively With Internal Audit and the First Line
- Treat Second-Line Challenge as a Core Financial Crime Governance Capability
Ultimately, the second line of defense is a core part of the financial crime environment because it provides the oversight and challenge that help keep the business within regulatory, policy, and risk boundaries. It is the layer that translates standards into monitoring and challenge, helping ensure that AML, sanctions, fraud, and wider financial crime controls are not only designed, but also applied consistently and credibly in practice.